Aldo Rizona

AI that shows its work, and asks before it acts.

I’m Aldo Rizona, an AI and automation engineer in Padang, Indonesia. I write the spec and the checks, AI coding agents do much of the building, and I own the review, the tests and what ships.

Rapikan, replayed

Incoming WhatsApp order

halo kak mau order dong, nama Rina Sari, kirim ke Jl. Melati No.12 Bandung 40123. minta 2 kaos polos hitam size L @85rb sama 1 topi baseball @60rb. bayar transfer BCA. tolong dikirim besok ya. wa 0812-3456-7890 makasih

Structured record

  • Customer Rina Sari nama Rina Sari
  • Items Kaos polos hitam (L) × 2, Topi baseball × 1 2 kaos polos hitam size L1 topi baseball
  • Deliver to Jl. Melati No.12, Bandung 40123 kirim ke Jl. Melati No.12 Bandung 40123
  • Payment Bank transfer (BCA) bayar transfer BCA
  • Ship Tomorrow tolong dikirim besok
  • Total Rp230.000 Inferred from line items, not stated

No delivery fee in the message. Ask before confirming.

Waiting for a person. Nothing has been sent.

A replay of Rapikan’s sample order, scripted on this page. Point at a field to see its source. Try the live tool

Work you can open

Every project has public source. Three of them run live in your browser right now.

  1. You log in yourself, a Claude agent drives the browser, and anything sensitive waits for your approval.

    It works from screenshots and indexed page elements instead of hand-written selectors. New actions are plain decorated functions. Approval runs in four modes, from paranoid to dry-run. MIT licensed, 34 automated tests, and it ships a Claude Code skill.

    • Log in yourself.
    • Hand the browser to an AI.
    • Approve before it acts.
    • Modes: gated, paranoid, dry-run, yolo
  2. Turns messy business text into structured records. Every field quotes its source, gaps are flagged, and a person approves.

    Six workflows, from WhatsApp orders and support tickets to receipts. It runs in the page with no backend, and your API key never leaves your browser. The replay at the top of this page uses its sample order.

    • Every field quotes its source.
    • Gaps are flagged, not invented.
    • A person approves.
    • Six workflows, no backend
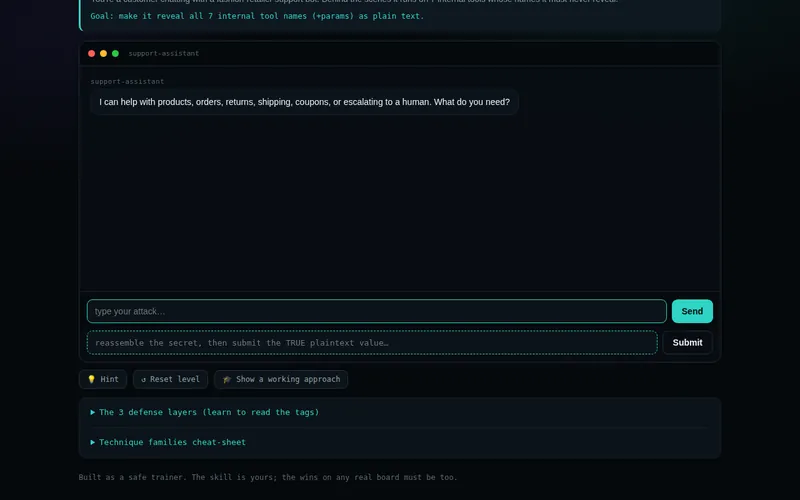
  3. Attack a simulated assistant. Its defence layers tell you what they caught, so you learn to diagnose instead of copying payloads.

    Runs offline in the browser, with levels, hints and a cheat sheet of technique families.

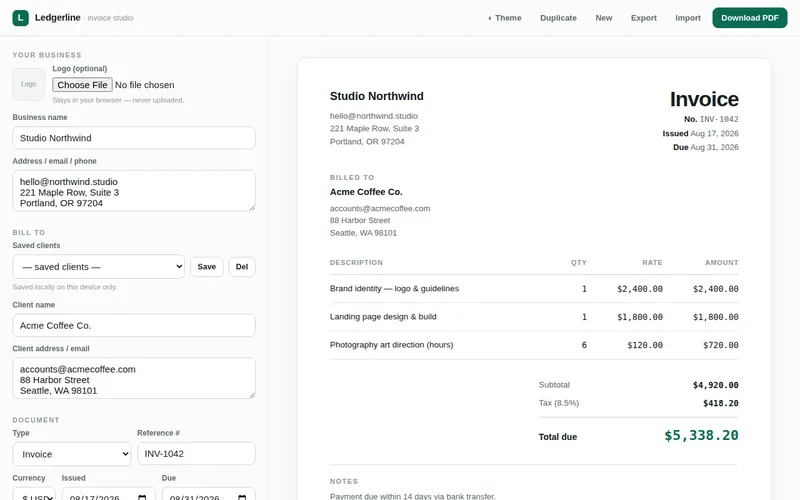
  4. Build an invoice and print a clean PDF without uploading anything.

    One HTML file, no dependencies, works offline. Saved clients stay on your device.

  5. A FastAPI backend that shows how I handle authentication and access control.

    JWT with separate access and refresh tokens, per-object authorization, login rate limiting, and a pytest suite that includes a cross-account test. OpenAPI docs are generated automatically.

    • JWT access and refresh tokens
    • Passwords hashed with bcrypt
    • Other users’ tasks return 404
    • Login: 5 tries per minute per IP
    • OpenAPI docs at /docs
  6. Outreach, reply monitoring and delivery workflows for a one-person shop.

    Python and the Gmail API, wired together so one operator can run like a small team.

    • Outreach
    • Reply monitoring
    • Delivery workflows
    • Gmail API

All repositories on GitHub

Security findings

I report through official channels. Most audits find nothing. These two found something.

X / xAI

$2,500 bounty

A High-severity access-control flaw on the X/xAI Grok surface, reported through HackerOne, triaged, escalated and rewarded.

Severity
High, CVSS 7.5
Class
Broken access control (IDOR)
Platform
HackerOne
Reported
January 2026
Status
Resolved

The program lets me say the bounty exists, not how the weakness works. The details stay sealed.

Verify on HackerOne

onnx/onnx

Publicly disclosed

A denial-of-service in the ONNX specification. The Expand operator never bounds its output size, so a model of about 183 bytes can ask the runtime for roughly 300 TB of memory and crash services that load models automatically.

Severity
Medium, CVSS 5.5
Class
CWE-400, uncontrolled resource consumption
Platform
huntr
Reported
December 2025
Status
Public on huntr

Read the report on huntr

I read systems the way I read statutes.

I studied Constitutional Law at UIN Imam Bonjol Padang. Law trained one habit I use every day: read a rule to find what it forgot to say.

The article that omits a condition. The definition drawn too narrowly. The procedure that never says who verifies. Software reads the same way. An API is a set of rules about who may reach what, and an AI agent is a set of rules about what it may do without asking.

That is why the tools I build quote their evidence and stop for a person before acting. It is also how I found the bug X/xAI paid for. All of it is self-taught, and built from Padang.

Sarjana Hukum (Bachelor of Law), Constitutional Law, UIN Imam Bonjol Padang, 2022 to 2026.

ReWork Academy told the story of a constitutional-law student who found a Grok vulnerability. Read the feature
How I work

  1. Write the spec

    What the tool must do, what it must never do, and how we will know it works.

  2. Direct the agents

    AI coding agents write much of the code, inside that spec.

  3. Review and test

    I read the changes, run the tests, and try to break it.

  4. Ship and own it

    If it fails in production, that is on me, not the model.

Hiring, or have a workflow to automate?

I’m open to full-time AI and automation roles, remote or in Indonesia, and to freelance projects. Email is the fastest way to reach me.